China’s Ministry of Industry and Information Technology (MIIT) has opened a public consultation on Requirements for Vehicle Data Security, a proposed mandatory national standard that would replace GB/T 44464—2024, General Requirements for Vehicle Data. Comments are accepted until December 19, 2026. The proposal would combine manufacturer governance, vehicle-level technical controls and inspection methods, with implications for automotive semiconductor, connectivity hardware and software suppliers. MIIT consultation notice
The draft, numbered GB 44464—XXXX, remains subject to revision. Its drafting explanation recommends July 1, 2028 as the implementation date, but this is not a confirmed deadline. Newly applying vehicle models would comply from the effective date, while previously approved models would begin applying the requirements in the thirteenth month afterwards.
The proposal applies to M- and N-category vehicles, excluding specified special-purpose vehicles modified from already approved chassis or complete vehicles. Although its principal obligations concern vehicle manufacturers and products, supplier capabilities and documentation would support manufacturers’ compliance.
Data security requirements would reach component integration
Manufacturers would establish vehicle-function data-processing inventories, assess risks, implement protective measures and verify their effectiveness. Partner management would include capability assessments, security agreements and performance supervision.
For suppliers, BESTAO expects this to generate more detailed customer requests covering interfaces, processing functions, security controls and lifecycle support. However, the draft does not establish a separate certification scheme for automotive chips or require domestically manufactured semiconductors.
Onboard important data and sensitive personal information would require protection against unauthorised access through secure access controls, encryption or other security technologies. Offboard transmission of these data categories would require confidentiality protection.
Automotive chip suppliers should therefore explain how their components support the customer’s chosen architecture, including memory protection, access isolation and cryptographic operations where available. Component capabilities alone would not demonstrate vehicle compliance: configuration, firmware and integration determine whether protection works.
Connectivity hardware and software face endpoint scrutiny
Clause 6.8 proposes that vehicles must not directly transmit data overseas, with exceptions for specified autonomous user activities, including browsing foreign websites and sending messages abroad through communications software.
This provision is relevant to telematics control units, connectivity modules, communications middleware and cloud-integration software. Manufacturers would need to understand where vehicle-originated traffic terminates, including diagnostic uploads, analytics and remotely configured services.
BESTAO recommends that suppliers document destination configuration, communication paths and update mechanisms. A connection’s encryption strength does not resolve whether its receiving destination is permitted. Likewise, routing through a domestic server should not automatically be treated as satisfying all subsequent cross-border obligations.
Software must enforce permissions and minimise collection
The draft generally requires personal-information collection to be off by default, subject to user settings and specified exceptions. Inactive functions must not invoke unnecessary camera, location or microphone permissions. Vehicles must also record and centrally display relevant sensor usage.
These requirements could affect operating systems, drivers, middleware and diagnostic software. Suppliers should assess whether background services collect data before function activation or continue processing after consent withdrawal.
Sensor coverage and resolution must correspond to functional needs. This creates documentation implications for camera-processing, radar and other sensing suppliers, rather than a general prohibition on high-performance devices.
Change management becomes a commercial priority
The same-type provisions reference controller manufacturers, hardware models, software versions, sensor configurations and anonymisation algorithms. Certain changes qualify for direct equivalence; others may require supplementary inspection and testing.
A substitute chip or firmware release could consequently affect approval evidence if it changes processing, monitoring or protection behaviour. Suppliers should provide clear change descriptions and support customers’ impact assessments.
BESTAO Analysis & Recommendations
BESTAO considers that suppliers should prioritise three activities: map component-level data flows, prepare evidence supporting vehicle tests, and establish customer-facing change controls.
Particular attention should go to diagnostic buffers, debug interfaces, persistent logs, transmission destinations and deletion behaviour. Connectivity suppliers should clarify responsibility between hardware, embedded software and backend services. Semiconductor suppliers should distinguish supported security features from controls requiring customer implementation.
Early cooperation with vehicle manufacturers can help identify integration gaps before testing. For Chinese or English versions of the draft and supporting documents, or a supplier-specific assessment, please contact BESTAO.
Top Read Articles
Switch articles-
 12-November-2026
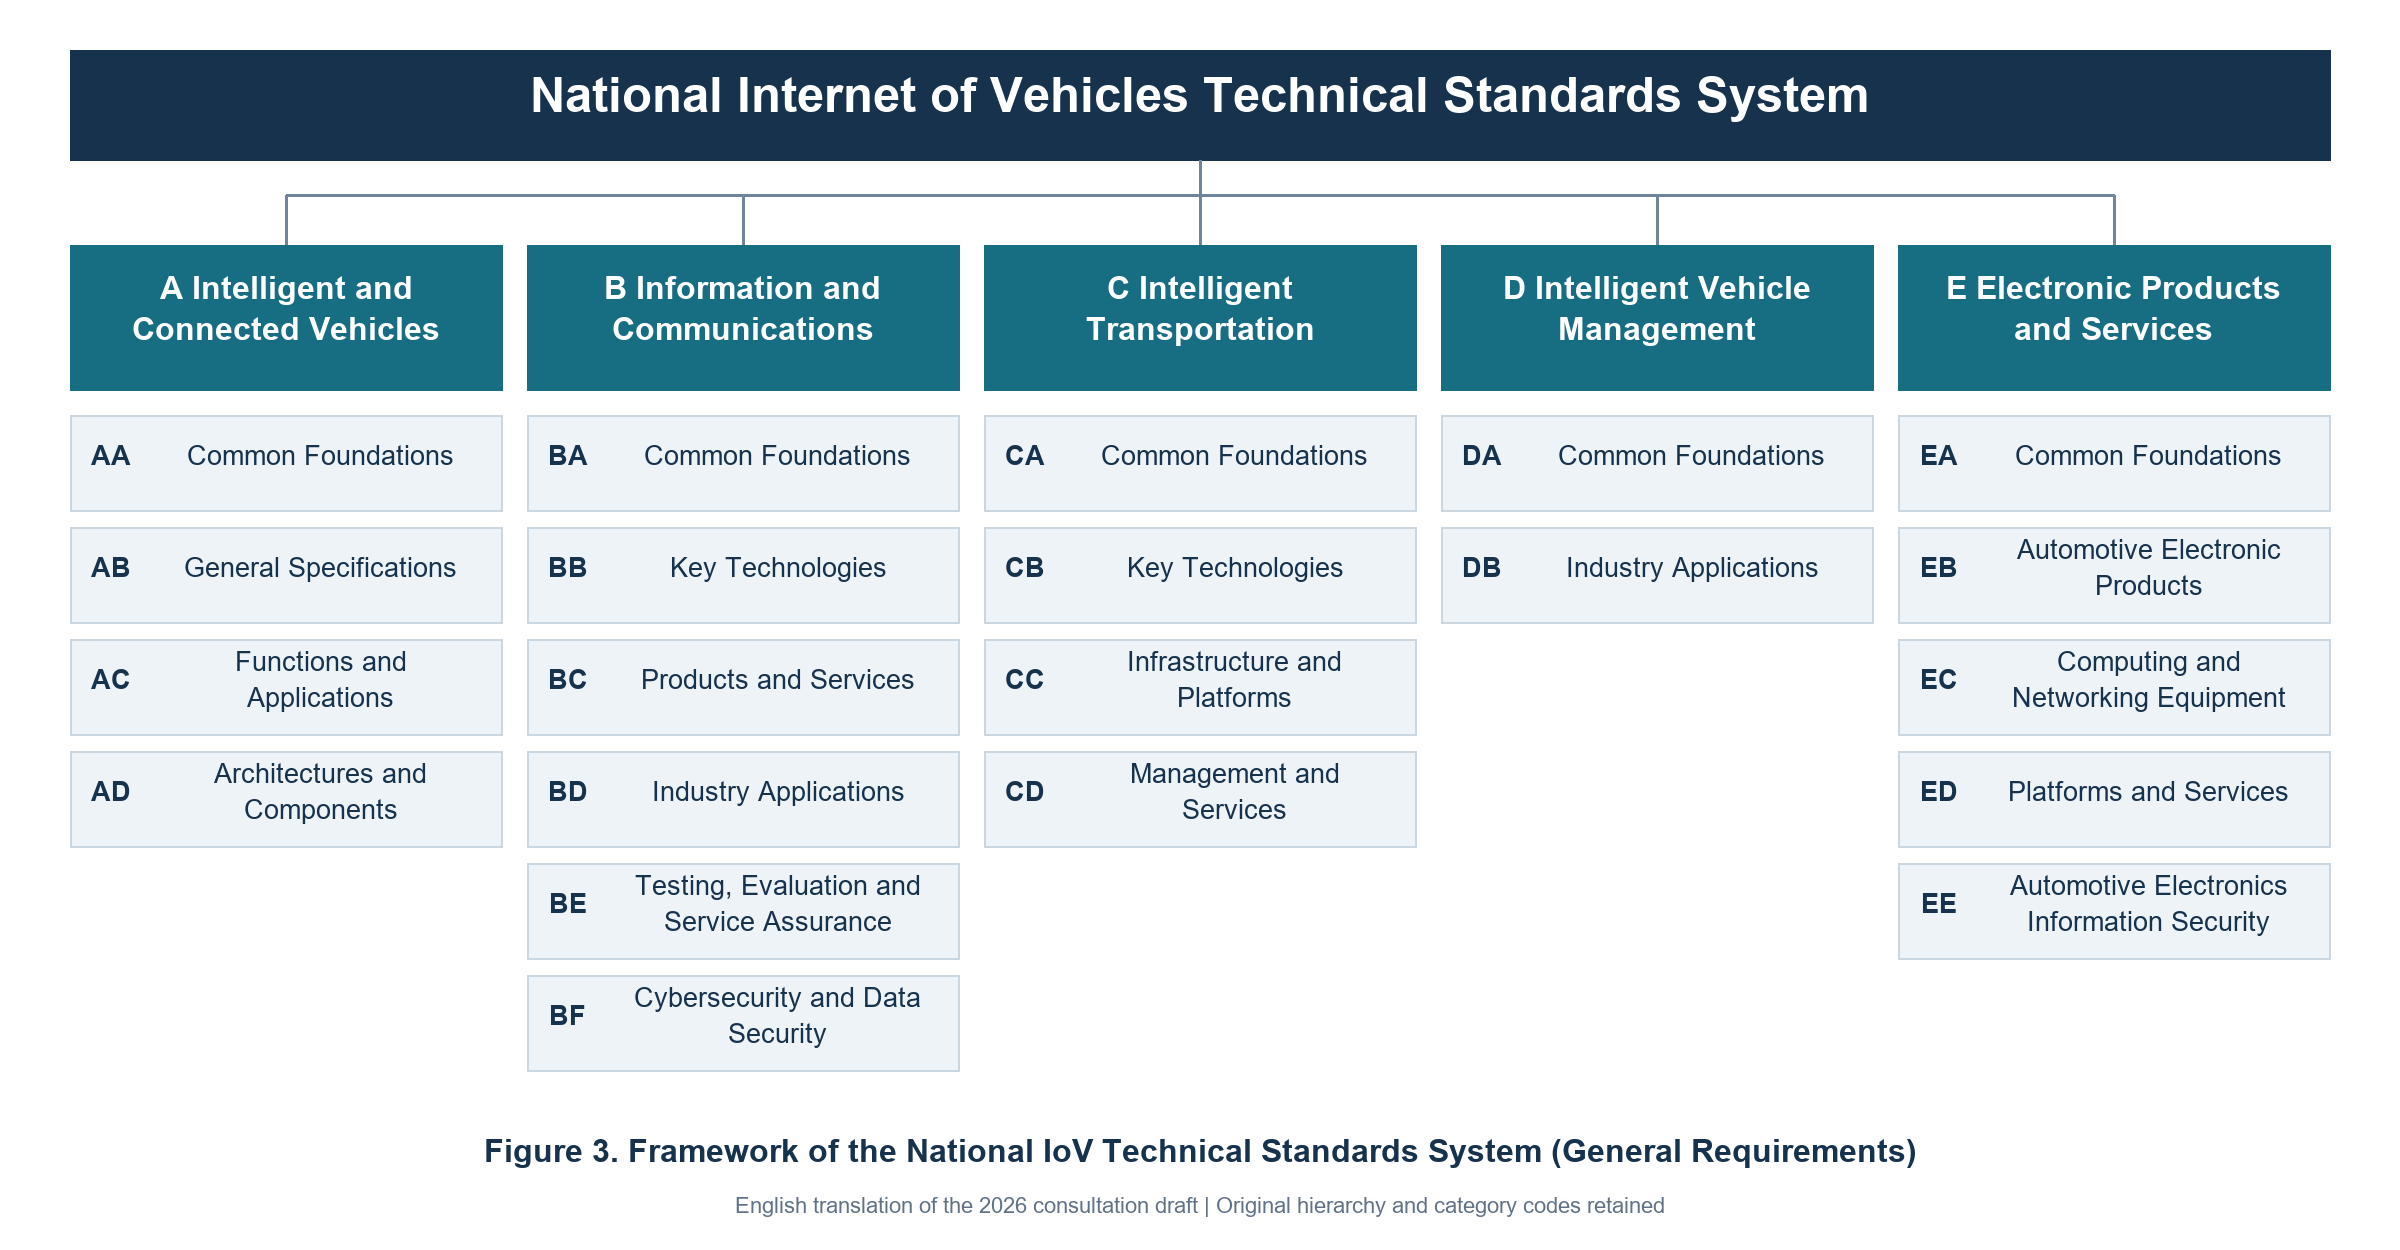
China Proposes Updated Internet of Vehicles Standards Roadmap Through 2030
-
 11-November-2026
China’s MIIT Establishes Industrial Software Standards Committee
-
 10-November-2026
China Sets New Mandatory Vehicle Geospatial Data Security Requirements
-
 10-November-2026
China Implements 4 Revised Mandatory Toy Safety Standards
-
 04-November-2026
New China WEEE Rules Proposed to Strengthen Producer Responsibilities