China operates a well-established data export security management framework, anchored by the Personal Information Protection Law (PIPL), the Data Security Law, the Cybersecurity Law, and Regulations on Network Data Security. Under this framework, companies transferring data out of the country have three lawful pathways: (1) passing the security assessment organized by the Cyberspace Administration of China (CAC); (2) obtaining personal information export certification from a professional certification institution; and (3) signing a standard contract with the overseas recipient based on the template issued by the CAC. This article will dissect the second pathway, which is the personal information export certification.
What Is Personal Information Export Certification?
Personal information export certification is a conformity assessment activity under Article 38(1)(2) of the PIPL, conducted by professional certification bodies legally qualified for personal information protection certification. It demonstrates that a handler's cross-border personal information processing activities comply with applicable laws, administrative regulations, departmental rules, standards, and technical specifications.
Who Should Use This Pathway?
According to the CAC, non-critical information infrastructure operators (non-CIIOs) that have cumulatively provided, since January 1 of the current year, personal information of more than 100,000 but fewer than 1 million individuals (excluding sensitive personal information), or sensitive personal information of fewer than 10,000 individuals, and whose data does not include important data, may fulfill their compliance obligations through certification.
Certification is also available on a voluntary basis. Regardless of export volume, any handler may apply to a professional certification body to demonstrate compliance with GB/T 35273 Information security technology – Personal information security specification and GB/T 46068 Data security technology – Security certification requirements for cross-border processing activity of personal information, thereby strengthening its overall compliance posture.
The CAC has warned against circumvention: handlers must not split data volumes to channel information that should undergo security assessment into the certification pathway instead.
Scaling Up: From Certification to Security Assessment
Companies should monitor export volumes throughout the year. If cumulative exports reach 1 million or more individuals' personal information (excluding sensitive data), or 10,000 or more individuals' sensitive personal information, the handler must file for a security assessment through the provincial cyberspace administration to the CAC. When filing, handlers may attach their certification results to demonstrate the protection levels of both themselves and their overseas recipients. The cyberspace authorities will take these results into account during the assessment.
How to Apply
Before applying, handlers must fulfill their statutory obligations under the PIPL, including informing data subjects, obtaining separate consent, and conducting a personal information protection impact assessment.
Currently, handlers may apply to any of the following certified institutions:
- China Cybersecurity Review, Certification and Market Regulation Big Data Center
- Data and Technical Support Center of the Cyberspace Administration of China
- Beijing CESI Certification Co., Ltd.
Conclusions
Personal information export certification is one of the three lawful pathways for moving personal information out of China, with clearly defined applicable scenarios, transition rules, and application procedures. Enterprises exporting personal information should carefully review the cumulative thresholds and requirements set out above and select the compliance pathway that matches their data export activities.
If you have any question or need further assistance, please reach us at: info@bestao-consulting.com
China Sets New Mandatory Vehicle Geospatial Data Security Requirements
China’s Draft Mandatory Vehicle Data Security Standard: Implications for Automotive Chip and Connectivity Suppliers
China Consults on Six National Standards for Identifying Important Data
Top Read Articles
Switch articles-
17-November-2026
China Consults on Six National Standards for Identifying Important Data
-
 16-November-2026
China’s MIIT Sets Out Industrial Carbon Control Framework with 400 Product Footprint Rules and Standards
-
 15-November-2026
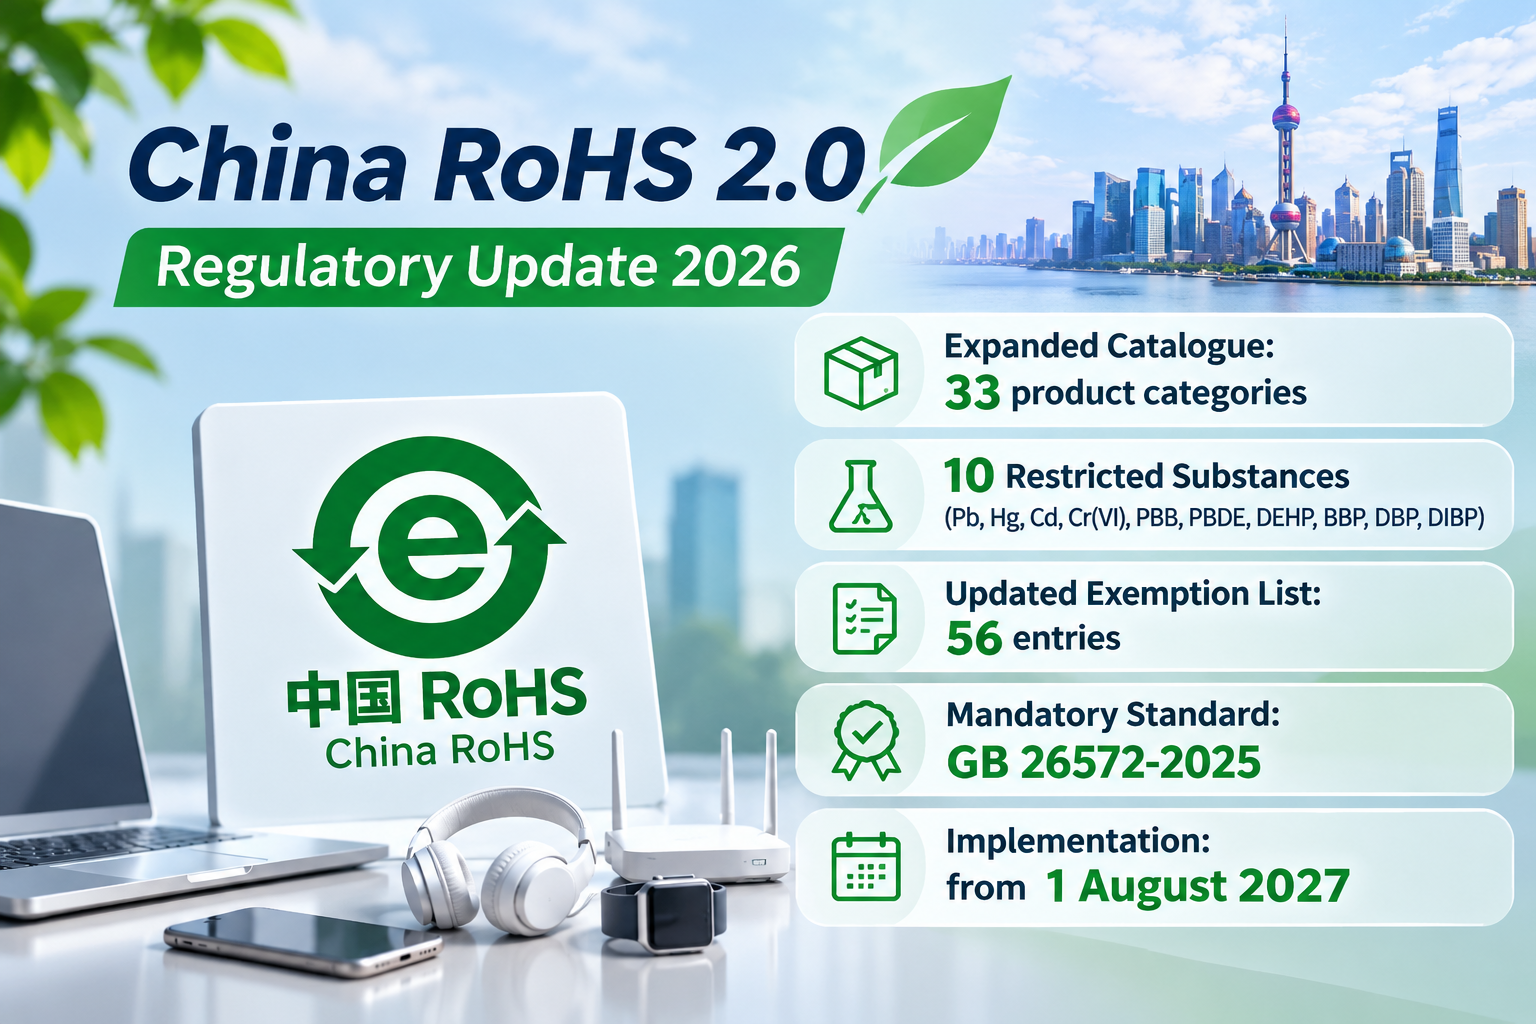
BESTAO Regulatory Update - China RoHS Enters a New Era
-
 12-November-2026
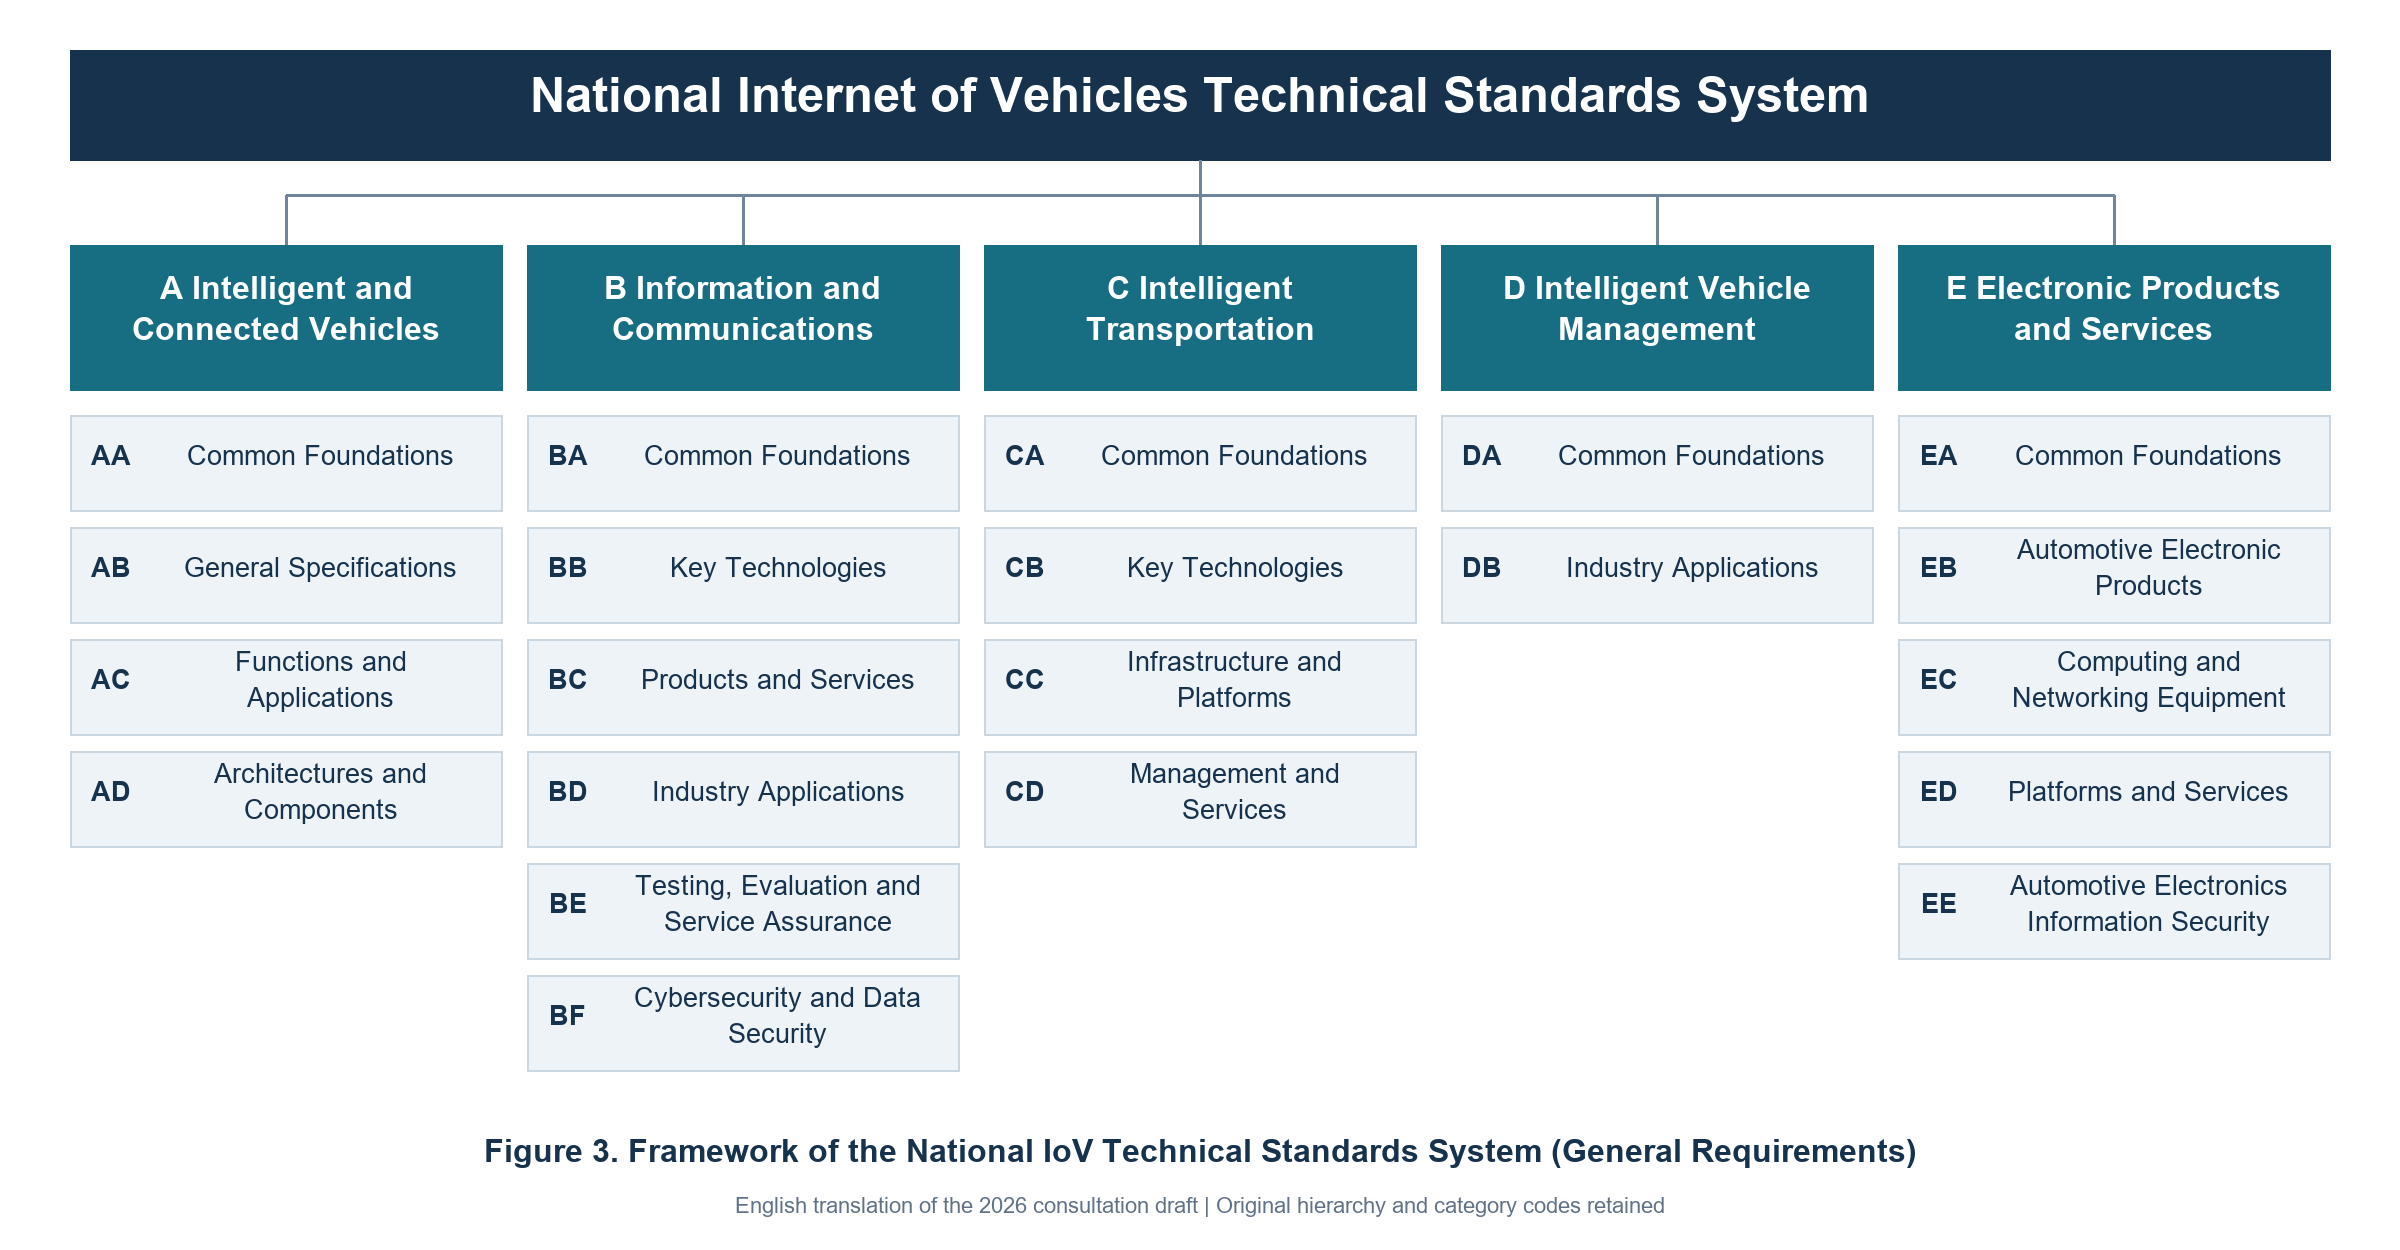
China Proposes Updated Internet of Vehicles Standards Roadmap Through 2030
-
 11-November-2026
China’s MIIT Establishes Industrial Software Standards Committee